[ad_1]
Simulating transfers utilizing security instruments inside crypto wallets can present a small achieve even when the ultimate transaction sends the consumer’s deposit to an attacker, in line with a July 30 arXiv preprint that hyperlinks the approach to five,742 sufferer addresses and about $3.48 million in historic losses.
The authors used SimGuard, a contract-bytecode detector, to establish 4,224 transaction-simulation phishing contracts throughout Ethereum, BNB Good Chain, Avalanche and Polygon.
The examine related them with 6,223 sufferer transactions however referred to as the loss estimate an higher certain as a result of some attacker take a look at exercise could have been misclassified. It attributed 91.5% of the losses to Ethereum and about 83% of the cross-chain whole to its largest inferred cluster.
The findings haven’t been peer reviewed. The paper additionally provides inconsistent figures for its Avalanche contract depend and conflicting endpoints for the commentary interval, leaving its per-chain breakdown and actual time window unresolved.
How a safe-looking preview can diverge
Transaction simulation takes a pre-signing snapshot of what a transaction is predicted to do. The contracts described within the paper include branches that may produce one end result throughout that verify and one other when the transaction executes on-chain.
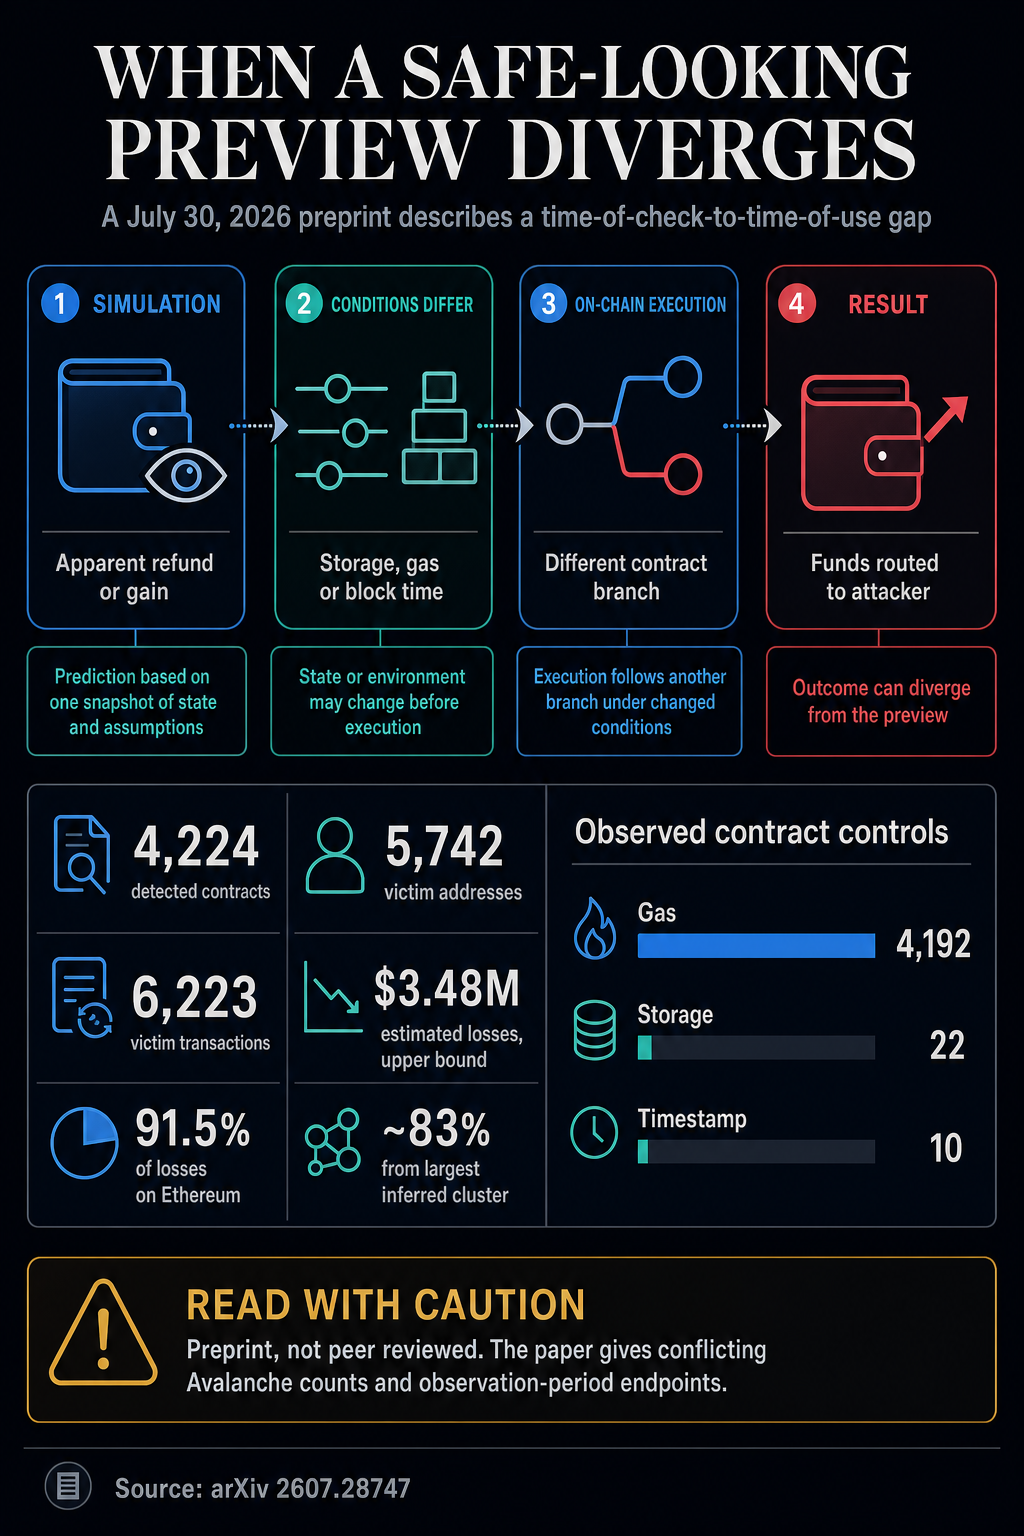
In a storage-control instance, the simulation returns the consumer’s deposit plus a tiny reward. An attacker can then change the contract’s state, corresponding to by blacklisting the consumer’s deal with, earlier than the transaction lands. The executed department sends the deposit to an attacker-controlled deal with as a substitute.
Timestamp-based contracts can exploit the later block time, whereas gas-control contracts can behave otherwise when the simulator and remaining transaction use totally different fuel limits. Not each variant subsequently requires an attacker to change saved on-chain information after the preview.
In a managed take a look at, the authors despatched an account’s stability to a contract that returned as little as 1 wei, the smallest unit of ETH. They reported that a number of examined previews displayed a constructive estimate and most didn’t clearly present the total outgoing quantity.
The paper doesn’t establish the pockets variations, settings, or simulation backends utilized by the historic victims. MetaMask’s present documentation calls estimated stability adjustments predictions and warns that the ultimate consequence isn’t assured.
A Jan. 8, 2025 Etherscan transaction cited by the examine information a Declare() name transferring about 143.45 ETH via a contract Etherscan labels as phishing. The on-chain document helps the switch described within the paper, though it can not present what appeared within the consumer’s pockets preview.
The authors suggest re-running simulations when related contract state or fuel fields change, utilizing the fuel restrict and fuel worth within the precise request, and testing present and future block-number and timestamp inputs. Their UI findings additionally assist exhibiting the gross quantity leaving a pockets alongside an correct internet stability change, so a negligible refund can’t be mistaken for a revenue.
The preprint describes historic exercise, not a stay July or August assault wave. Its detector analysis lined 44 contracts, together with 30 generated with Gemini, and the linked code-and-data repository returned HTTP 401 when checked.
The mixture outcomes subsequently stay the authors’ findings moderately than an independently reproduced measurement.
[ad_2]
Source link
Frequently Asked Questions
What did researchers find about malicious smart contracts?
Researchers uncovered 4,224 malicious smart contracts that tricked 5,742 victims into signing away their crypto, resulting in approximately $3.48 million in losses. These contracts were identified across various blockchain platforms including Ethereum, BNB Smart Chain, Avalanche, and Polygon.
How do transaction simulation phishing contracts work?
Transaction simulation phishing contracts create a deceptive preview of a transaction, showing a positive outcome. However, when executed on-chain, they can redirect the user's deposit to an attacker-controlled address instead, often after manipulating the contract's state.
What percentage of losses were attributed to Ethereum?
The study attributed 91.5% of the total losses to Ethereum, indicating that the majority of the identified malicious activity and financial impact occurred on this blockchain platform.
What are the implications of the study's findings?
The findings highlight significant vulnerabilities in transaction simulation practices within crypto wallets, suggesting that users may be misled by previews that do not accurately reflect the final transaction outcomes, potentially leading to substantial financial losses.
Did the study undergo peer review?
No, the findings presented in the study have not been peer-reviewed. Additionally, the paper contains inconsistent figures and unresolved details regarding the contracts and observation periods.


